· javascript
Website management platform Optimizely confirms hackers put malicious code into customer sites
A breach at a popular website management company exposed customers’ visitors to malicious code that stole cryptocurrency and attempted to skim payment cards or install malware.
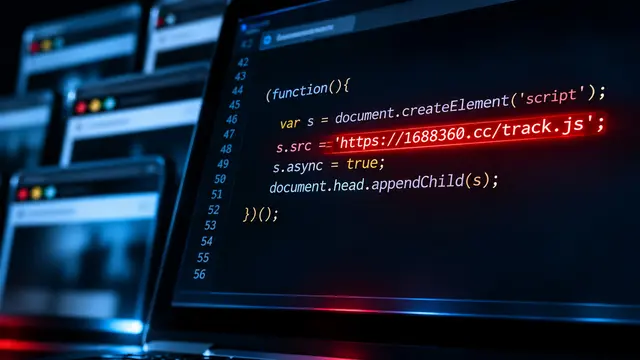
Researchers at cybersecurity firm Report URI said they found malicious JavaScript code on 178 different widely visited websites run through the Optimizely Web experimentation platform. Optimizely allows companies to personalize and manage their websites and apps. Optimizely confirmed the incident in a brief statement on Monday evening, writing that it “identified and contained a security incident affecting some Optimizely Web Experimentation customers.”
“The vulnerable path is blocked, the injected code was removed, and customers have been contacted directly,” the company said. It did not respond to requests for comment about the specifics of Report URI’s study. In a technical advisory, Optimizely confirmed Report URI’s findings that a vulnerability in its Experimentation platform allowed threat actors to inject malicious JavaScript into some customers’ websites.
Report URI listed dozens of prominent companies impacted by the breach and used blockchain evidence to track at least $7,000 stolen through the malicious code. “The malware was a multi-purpose kit. It swapped cryptocurrency wallet addresses for the attacker's, skimmed payment cards, stole cookies and screenshots, and on iPhones and iPads it delivered the Coruna and DarkSword iOS exploit kits.