· ai-devtools
Microsoft agent-framework Python versions 1.26.1, 1.26.2 contain credential stealer
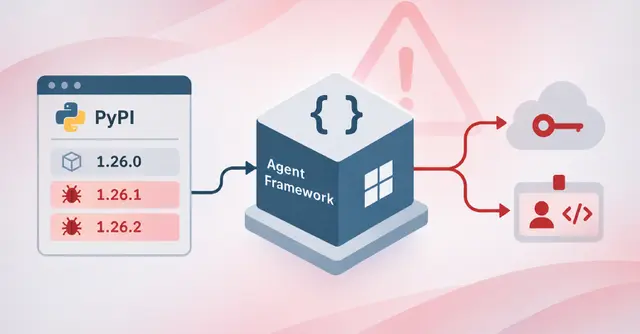
Malicious code designed to pilfer cloud and CI/CD credentials from developers’ machines was embedded within two versions of Microsoft’s official agent-framework package available on the Python…
Malicious code designed to pilfer cloud and CI/CD credentials from developers’ machines was embedded within two versions of Microsoft’s official agent-framework package available on the Python Package Index (PyPI). This framework, which serves as Microsoft's open-source toolkit for constructing and executing AI agents within various workflows, was compromised. Three distinct supply chain security firms—StepSecurity, OX Security, and Socket—were responsible for detecting these tainted releases and subsequently disseminating their findings. The discovery was first made public via a post on Help Net Security, detailing that “On November 17, 2026, versions 1.26.1 and 1.26.2 of the official Microsoft agent-framework package on PyPI were published.”
Why it matters
This incident highlights critical supply chain vulnerabilities within widely used open-source tools like Microsoft's Agent Framework. Developers must immediately audit dependencies and understand the risks associated with package integrity on PyPI.