· ai-devtools
Elastic Security Threat Command finds hackers need 8 minutes to log in with stolen credentials
In 27 verified instances of infostealer activity, threat actors managed to use pilfered login details just eight minutes on average following the initial compromise, a finding detailed in a report…
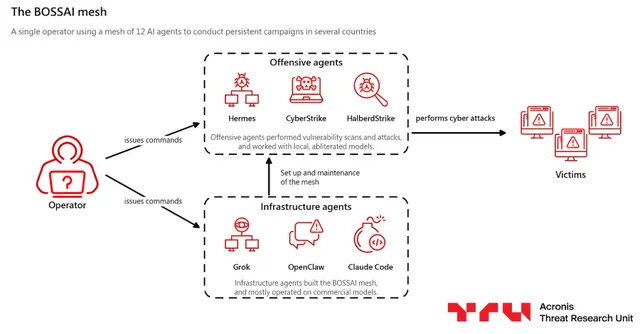
In 27 verified instances of infostealer activity, threat actors managed to use pilfered login details just eight minutes on average following the initial compromise, a finding detailed in a report issued by Elastic Security Threat Command. Furthermore, the investigation uncovered instances where AI applications were exploited to run commands and where digitally signed remote monitoring utilities were employed to sustain unauthorized access. Regarding these findings, one expert noted, “An agent that holds credentials and can reach the internet is a new attack surface, whether it’s misconfigured or abused. When an attacker is behind it, its activity...”. This information, which suggests a rapid window for credential exploitation, was initially published on Help Net Security.
Why it matters
This highlights the speed at which attackers can leverage stolen credentials, emphasizing the urgency of credential security practices. Developers must be aware that compromised agents with internet access present a significant new attack surface.